
Real-time Protection for Magento
Protect your store from all known Magento attacks.* Save thousands in developer time. Avoid downtime and instability from rushed patching.
Unlike traditional WAFs that rely on generic rules, Sansec Shield deeply integrates with Magento and benefits from Sansec's famous expertise in Magento security. This makes our WAF the most effective solution to protect your Magento store.
Protection rules update automatically as our researchers identify new threats, without extra deployments or manual configuration.
Hack Protection Guarantee
We guarantee your store won't be hacked while Shield is active. See FAQ below for guarantee conditions and requirements.
Patch on your schedule
No more emergency weekend deployments or rushed fixes that could break your store.
Instant Threat Protection
Block critical vulnerabilities as soon as they're discovered. When Amasty shipped a patch for an unauthenticated file upload flaw, Shield had already blocked over 12,000 exploitation attempts within hours.
How Shield Compares to Other WAFs
Feature-by-Feature Comparison
| Sansec Shield | Adobe Fastly WAF | Cloudflare | |
|---|---|---|---|
| Origin Protection | ✅ Bypass not possible | ❌ CDN, Direct integration with your application provides superior protection compared to CDN WAF solutions, which can be bypassed if attackers discover your origin servers. | ❌ CDN, bypass possible |
| Response Time to New Threats | ✅ Minutes | ❌ Adobe's WAF filters lag Sansec by months. Sansec added PolyShell (CVE-2026-48356) protection to Shield on March 16th. Adobe didn't ship a backported fix to supported Magento releases until July 14th, four months later. See the timeline | ❌ Cloudflare shipped a SessionReaper filter 34 days after Sansec. For PolyShell (CVE-2026-48356), Cloudflare has no published filter, months after Sansec added protection. See the timeline |
| Performance Impact | ✅ 0 ms | ❌ Adds proxy latency (no published figures) | |
| Setup Complexity | ✅ Simple Module Install | ✅ Simple (DNS only) | |
| False Positives | ✅ None | ❌ Yes | ❌ Possible (generic ruleset) |
| Filtering Transparency | ✅ Full Open Source | ❌ Mostly Closed Source | ❌ Closed Source |
| Supports | Adobe Cloud, Adobe Commerce, Magento Open Source | Adobe Cloud only | ❌ Platform-agnostic (no Magento focus) |
Shield vs Cloudflare and Other Generic WAFs
Cloudflare and other generic WAFs are not built for Magento. They rely on broad, industry-agnostic rules and typically only start filtering an attack after Sansec, or another vendor, has already published a fix. Sometimes that takes months. Sometimes it never happens.
StyleSmuggler (CVE-2026-75650)
Unauthenticated RCE in Magento & Adobe Commerce
September 5, 2026
Sansec Shield
Protection deployed
September 7, 2026 · 2 days later
Adobe
Emergency hotfix (APSB26-146)
September 10, 2026 · 5 days later
Cloudflare
WAF rule added (changelog)
September 10, 2026 · 5 days later
Imperva
WAF protection announced (announcement)
See the full timeline.
PolyShell (CVE-2026-48356)
Unrestricted file upload in Magento's REST API
March 16, 2026
Sansec Shield
Protection deployed
March 27, 2026 · 11 days later
Akamai
WAF rule added
July 14, 2026 · 4 months later
Adobe / Fastly
Backported patch (APSB26-73)
No published WAF rule
Cloudflare
See the full timeline.
SessionReaper (CVE-2025-54236)
Unauthenticated RCE in Magento & Adobe Commerce
August 19, 2025
Sansec Shield
Protection deployed
September 9, 2025 · 21 days later
Adobe / Fastly
Public patch (APSB25-88)
September 22, 2025 · 34 days later
Cloudflare
WAF rule added (changelog)
See the full timeline.
Shield doesn't replace Cloudflare or Fastly. Keep them in place for DDoS protection: Shield covers the Magento-specific layer, a generic WAF covers the network layer. There's no downside to running both.
Save Thousands in Dev Costs
Each patch takes a day. Shield protects you while you postpone, saving up to $5,000/year per store.
Magento-Exclusive Protection
Generic WAFs miss platform-specific threats. Shield doesn't, because we know Magento better than anyone.
Built for Stability
No more rushed updates, staging bugs, or patch regressions. Shield keeps your stack calm and secure.
* Sansec Shield protects against all Magento-level attack methods previously identified by Sansec. Should a new attack bypass Shield, Sansec will investigate and perform a cleanup free of charge. The guarantee requires an active Advanced or Enterprise license, the latest Shield module, and standard security hygiene. It does not cover third-party software, stolen credentials, or attacks via non-web channels. See full conditions below.
Installation
The Shield composer module requires Magento 2.3+, PHP 7.2+ and a Sansec Advanced or Enterprise license key.
# Install Shield module
composer require sansec/magento2-module-shield

# Configure Magento
bin/magento setup:upgrade
bin/magento config:set sansec_shield/general/license_key YOURKEY
bin/magento cache:clean

# Sync protection rules
bin/magento sansec:shield:sync-rules
Test it by visiting your store and add ?SANSEC-SHIELD-TEST to your URL.
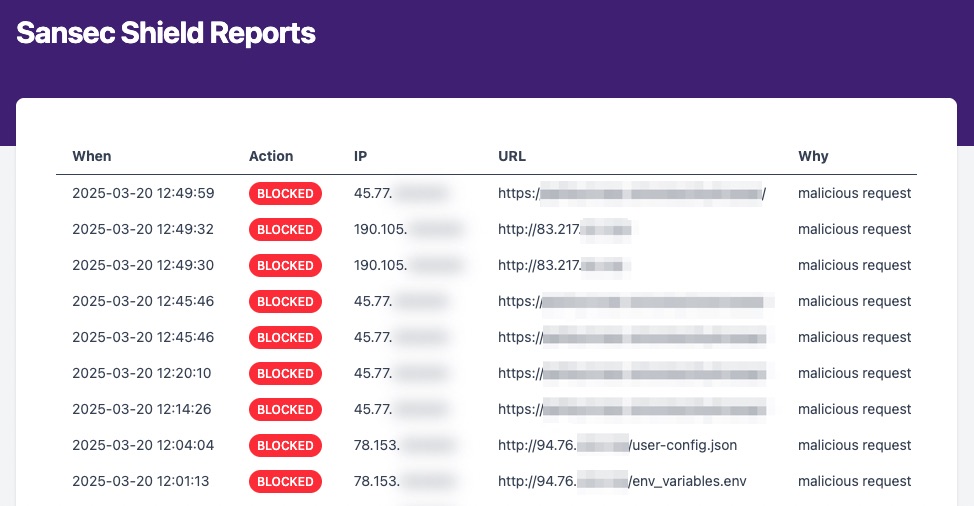
You'll see your first blocked attack appear instantly on your Shield Dashboard.
Having issues? Check our Troubleshooting guide.
Frequently Asked Questions
★Who can use Sansec Shield?
Sansec Shield is available for Adobe Commerce and Magento 2 stores with our Advanced plan or higher. Compatible with Magento Open Source and Adobe Commerce, including Adobe Cloud.
★Do I still need eComscan?
Yes. Sansec Shield protects against web traffic attacks, but attacks can come through other channels like compromised SSH accounts, hijacked devices, or non-Magento applications. Shield and eComscan work together to provide complete security coverage.
★We use Cloudflare WAF. Is Sansec Shield recommended and compatible?
Yes to both. Cloudflare is a generic WAF and consistently lags behind on Magento-specific attacks, sometimes by months, sometimes indefinitely. See how Shield compares to Cloudflare and other generic WAFs for real examples. Keep Cloudflare in place for DDoS protection: Shield covers the Magento-specific layer, Cloudflare covers the network layer, and there's no downside to running both.
★Does Sansec Shield impact store performance?
No. Shield has zero performance impact through efficient pattern matching, direct Magento cache integration, selective request analysis, and sub-millisecond processing times.
★How quickly are new threats added to protection rules?
Our global threat detection network identifies and distributes new protection rules within minutes of detecting attack patterns. All rules are automatically verified and deployed without manual intervention.
★How does Sansec Shield prevent false positives?
Shield only blocks actual attack probes - no secondary criteria like "suspect networks" or "suspicious user agents". Our Magento expertise means we know exactly what attacks look like. New detection rules are validated against hundreds of real stores before deployment.
★How quickly can we disable Sansec Shield?
No customer has ever needed to disable Shield, but if required, you can instantly disable it with this command (works on Adobe Cloud): bin/magento config:set sansec_shield/general/enabled 0
★What are the guarantee conditions?
Sansec Shield protects your store against all Magento attack methods that Sansec has previously identified. Should your store be compromised by a new Magento-level attack despite Shield being active, Sansec will investigate and perform a cleanup free of charge. This guarantee applies provided that:
- You have a valid Sansec Advanced or Enterprise license and run a supported version of Magento (v2.3+).
- You are running the latest version of the Sansec Shield module, and it is enabled and properly configured.
- You have changed your admin and database credentials since any previous attack.
- You have changed your encryption key since any previous attack.
- You enforce multi-factor authentication for staff accounts.
Our guarantee does not cover:
- Third-party applications and extensions (such as WordPress) running on the same server
- Attacks via secondary channels such as SSH, FTP, or compromised hosting accounts
- Abuse of stolen credentials or social engineering